
Docker View
Hosts, containers, logs, images, volumes, and available actions.
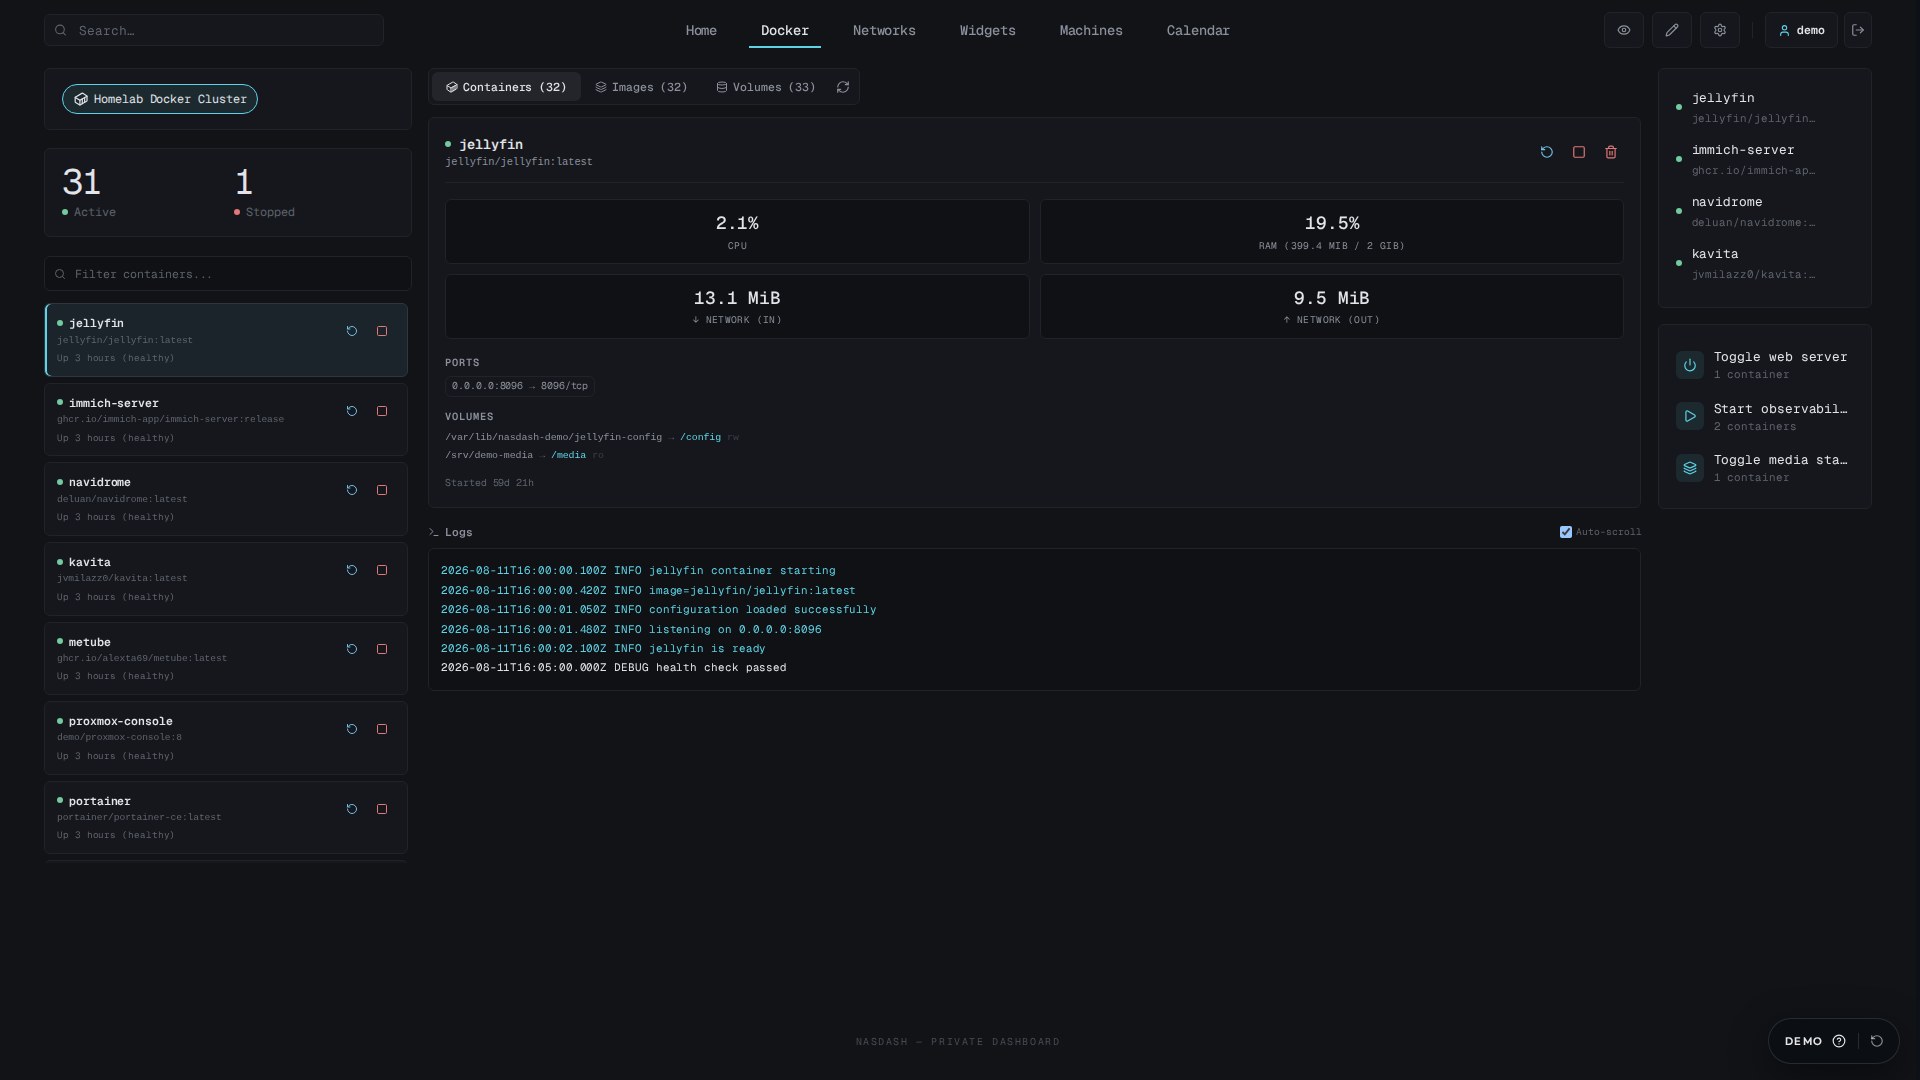
Configure hosts in Settings → Integrations. All connections are optional. Choose the route that fits your existing setup; Portainer and Dockhand do not need a socket proxy. Docker-compatible Podman APIs are also supported.
Connection choices
| Connection | Fields | Access |
|---|---|---|
| Portainer | Server URL, environment ID, dedicated API key | Docker API relayed through the selected environment |
| Dockhand | Server URL, environment ID, dedicated API token | Supported operations translated to its API |
| HTTP(S) API | Reachable engine or socket-proxy URL | Only operations allowed by that API or proxy |
| Unix socket | Absolute mounted socket path | Broad access to the engine; no proxy filtering |
Portainer uses the numeric environment/endpoint ID and an API key created for a dedicated account. Dockhand uses its environment ID and an API token. Use the server root URL, without appending an environment page or API path; NasDash adds the required path. Find the ID in the provider's environment details, not its display name. NasDash encrypts saved credentials; leaving the masked key unchanged when editing preserves it. Never share a token, include it in a URL, or post it in logs.
The NasDash server contacts the provider, not the browser. Save the host, select it in Docker hosts, and inspect its loading or error indicator; there is no Docker connection Test button. For the local proxy, use the container-side probe in its guide. Prefer a trusted certificate; accept self-signed certificates only for a connection you control.
Docker hosts widget
Administrators can add or edit a Docker actions shortcut in page edit mode. Name the action, choose its icon and operation, then select containers from the saved hosts; each target keeps its host association. Save the action. Running start or stop still requires administrator access and provider permission.
The Docker hosts widget shows the running and stopped container counters of the selected host under the host chips. In page edit mode, the # button shows or hides them. On a page that still has the former counters widget, the hosts widget leaves the counters to it; in edit mode, that old widget offers a Remove this widget button.
In page edit mode, each host chip has a pencil to edit the host (name, icon, connection and address) and a cross to remove it. Reorder hosts by dragging their handle; with the keyboard, press Space, use the arrow keys, then press Space again. When editing a Portainer or Dockhand host, leave the API key empty to keep the saved key. A newly added host is selected immediately; its chip shows a spinner while its containers load and an alert icon when the host cannot be reached.
Containers, images and volumes
The explorer shows containers, inspect details, available statistics and logs, images and volumes for the selected environment. Portainer relays the Docker Engine API; Dockhand translates its supported endpoints. The provider version, API-key permissions and environment must allow each requested operation. A denied or unsupported operation is an error, not evidence of an empty engine. Do not assume that a successful connection test grants deletion rights.
Images show available tags, digests, labels or their stable image ID. An unused image is not necessarily untagged; tagged images keep their names. If the engine no longer reports any tag, NasDash identifies the image as untagged and cannot reconstruct a removed historical name. Usage checks include stopped containers as well as running ones.
Mutations require an administrator and permission from the selected provider. The setting that shows Start/Stop buttons in widgets controls presentation, not API authorization. A socket proxy additionally limits permitted API methods. An attached volume or referenced image must not be removed; review the resource name and usage before confirming. Back up persistent volume data separately; an image list is not a backup. See access rules.
Use search to find a name, tag, image ID or linked container. Filter by usage (or untagged images), sort by name, creation date or reported size, and choose 5, 10, 25 or 50 resources per page. The default is five rows on mobile and ten on desktop; an explicit page-size choice is retained when the viewport changes. The page-selection checkbox is in the table header, including on mobile. Usage counts sit beside Refresh and wrap when needed; unused resources are marked in red. Expand a row to read all reported tags, digests, mount paths and linked containers; missing metadata is shown as not reported. The select-all checkbox selects only unused resources on the visible page. Selections persist between pages, but changing the search or usage filter clears them. Review the full target list in the confirmation; after a partial failure, retry submits only failed targets. Narrow widgets and mobile screens stack the same information instead of hiding actions. The information bubble beside the Images/Volumes title explains why resources linked to running or stopped containers are protected from deletion.
Optional local socket proxy
The socket proxy guide explains its restricted endpoints and private Docker network. Start its optional Compose profile:
docker compose --profile docker-proxy up -dChoose Address and fill the two fields separately:
Host  docker-proxy
Port  2375
The default Compose command starts only NasDash. Keep the profile enabled on recreates if your saved connection uses this proxy. Its POST=1 permits mutations and DELETE=0 disables deletions; use POST=0 for a read-only proxy. Never publish an unauthenticated Docker API. For another machine, see remote connections.
Direct Unix socket
Mount the socket into NasDash only when you intentionally choose direct engine access:
services:
  nasdash:
    volumes:
      - ./data:/app/data
      - /var/run/docker.sock:/var/run/docker.sock:ro
Keep your existing data mount; use the matching socket path in the connection and ensure the runtime user can access it. Podman commonly uses /run/podman/podman.sock; adjust both paths for the actual deployment. The :ro mount prevents replacing the file but does not make Docker API operations read-only. Portainer, Dockhand and HTTP API connections need no socket mounted into NasDash.